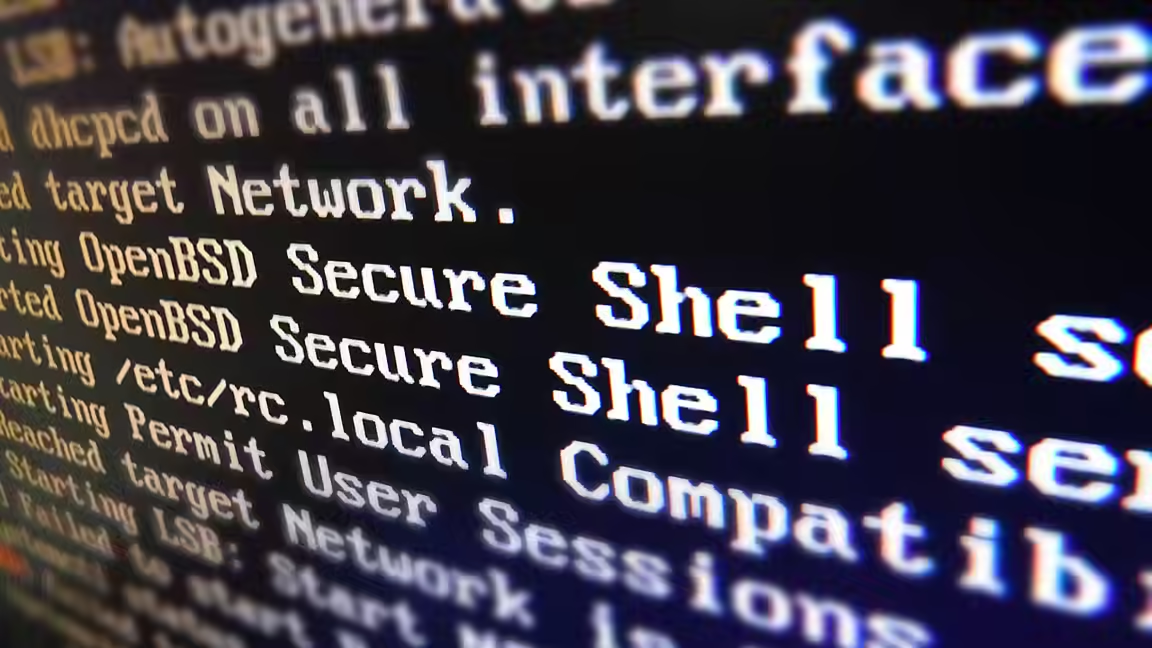
OpenSSH released version 10.6p2 with an emergency workaround for a critical password-authentication vulnerability affecting a narrow but important group of Linux installations. The project’s maintainer said systems that combine the musl C library with direct password authentication and no Pluggable Authentication Modules, or PAM, are exposed. Alpine Linux was cited as a prominent example of an operating system that can use that configuration.
The immediate advice is unusually blunt: administrators responsible for an affected host should set `PasswordAuthentication=no` or disable SSH access until the updated package is installed. The warning does not apply to non-Linux systems, Linux distributions based on glibc, or Linux installations that route password checks through PAM. Key-based access is not itself described as the vulnerable mechanism, but disabling password authentication is the stated containment step for potentially exposed servers.
According to OpenSSH maintainer Damien Miller, the underlying defect sits outside OpenSSH. The project nevertheless produced a mitigation because it is positioned to protect users quickly at the SSH layer. That distinction matters for remediation: the OpenSSH update is a practical defense, while operating-system and library maintainers may also need to address the behavior that made the authentication bypass possible.
The release was assembled rapidly after the report arrived. Miller said the team learned of the problem one day before announcing 10.6p2. He also explained that the project now views lengthy embargoes as risky because automated systems can independently rediscover software flaws within hours. The maintainers therefore chose a fast disclosure and mitigation cycle intended to reduce the window in which vulnerable systems remained unknowingly reachable.
The issue was reported by Özgün Kültekin of Wakefield, and Alpine Linux developers prepared an updated release on short notice. Operators should obtain packages from their distribution rather than assuming that changing a banner or restarting an older daemon applies the workaround. They should also verify the host’s C library and authentication path instead of inferring exposure solely from a distribution name.
The narrow scope should not be mistaken for low severity. Internet-facing SSH services are a primary administrative entry point, and an authentication bypass can erase the protection expected from a locked account. The affected combination may be uncommon across mainstream server distributions, yet it is plausible in lightweight containers, appliances and cloud images where musl and minimal authentication stacks are deliberate choices.
For mixed fleets, the safest triage is configuration-based: identify Linux hosts using musl, determine whether SSH password authentication is enabled, and confirm whether PAM handles those requests. Systems matching all three affected conditions deserve immediate action. After patching, administrators should retain the temporary restriction until the installed OpenSSH build and distribution advisory clearly confirm that the mitigation is present.